CyberArk Releases Framework for Rapidly Reducing Privileged Credential Risk
New CISO View Research Recommends a 30-Day Sprint to Mitigate Privileged Credential Vulnerabilities; Features Insights from Global 1000 CISOs and Post-Breach Experiences from Security…
New CISO View Research Recommends a 30-Day Sprint to Mitigate Privileged Credential Vulnerabilities; Features Insights from Global 1000 CISOs and Post-Breach Experiences from Security Experts
CyberArk Research: 30-Day Sprint to Mitigate Privileged Credential Vulnerabilities
CyberArk (NASDAQ: CYBR) today issued a new research report that recommends an accelerated 30-day plan to improve protection of privileged credentials. The report outlines a proven framework for rapid risk reduction based on lessons learned from several large data breaches and best practices from a panel of Chief Information Security Officers (CISOs) at Global 1000 enterprises.
The report, “Rapid Risk Reduction: A 30-Day Sprint to Protect Privileged Credentials,” is part of The CISO View industry initiative, sponsored by CyberArk. The CISO View conducts research and delivers peer-to-peer guidance from experienced executives to help security teams build effective cyber security programs. The report is the latest release in The CISO View series, featuring contributions from The CISO View panel: Top executives from ING Bank, CIBC, Rockwell Automation, Lockheed Martin, Starbucks, ANZ Banking Group Limited, CSX Corporation, Monsanto Company, Carlson Wagonlit Travel, SGX, News UK and McKesson.
The report also draws from the experiences of several of the major organizations that have suffered large data breaches. It features input from guest contributors including the security professionals and experts who were on the front-lines of breach remediation efforts.
Shutting Down the Privileged Pathway
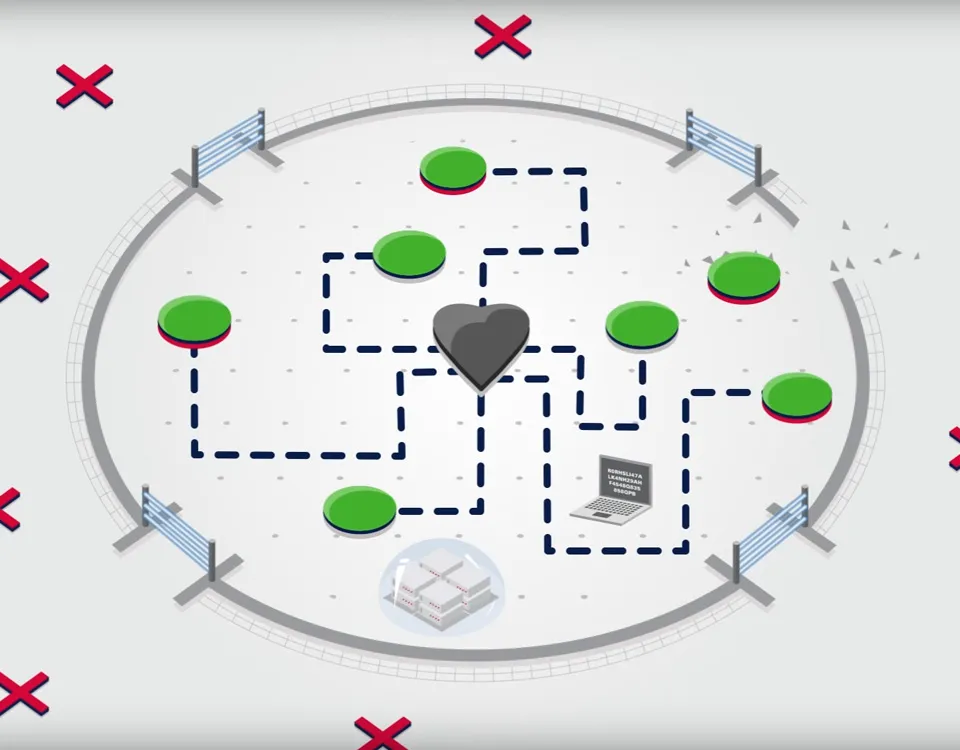
Attackers continue to demonstrate the ability to compromise privileged credentials to reach critical assets and steal sensitive data. In the incidents studied for this report, attackers were able to obtain domain-level Windows administrator credentials by exploiting common vulnerabilities found in most enterprise IT environments. Securing privileged accounts and credentials is one of the first actions organizations take following a breach to rebuild trust in their IT infrastructure.
“The number one thing adversaries do once they get into your network is look for the ability to escalate their privileges. Without good practices, you make it very easy for them to instantaneously traverse your whole network,” said Jim Connelly, vice president and CISO, Lockheed Martin.
The 30-Day Sprint Framework
The research identifies the common attack patterns and best practices that could have helped to prevent a breach in the first place. Based on these real-world experiences, the report recommends a fast-tracked initiative to help shut down the privileged pathway in Windows environments. It prioritizes the implementation of controls for protecting privileged credentials to drive tangible results within 30 days based on these goals:
- Identify accounts quickly – Locate administrator accounts in Windows using existing Active Directory and local Administrator groups.
- Give precedence to the riskiest accounts – Implement controls on the most powerful accounts first, such as domain administrator accounts and administrator accounts with access to large numbers of machines, as well as application accounts that use domain administrator privileges.
- Be realistic about addressing the volume of accounts – Work quickly to get initial controls in place and make improvements over time. For example, accounts for workstation users should not have administrative privileges, but breach survivors say this is one of the more difficult practices to implement and maintain due to the sheer volume of workstations.
Recommended controls include reconfiguring accounts to segregate duties, putting administrator passwords in a vault and requiring multi-factor authentication to access those passwords, removing workstation administrator privileges from end users, and implementing detection tools to look for signs of lateral movement or privilege escalation in real time.
“This CISO View report should be required reading for security teams and their executives who want to proactively protect their organizations from advanced attackers’ most-favored – and successful – techniques. Based on what we’ve seen in the field, combined with the shared experiences of participants, it is absolutely possible to drive results within 30 days,” said Gerrit Lansing, chief architect, CyberArk. “Collaboration and transparency are critical in effectively combatting cyber threats, and are key drivers behind The CISO View initiative. We value the efforts of the security experts and executives who contributed to this research to improve enterprise security strategies.”
For more information about “Rapid Risk Reduction: A 30-Day Sprint to Protect Privileged Credentials,” and the previous report, “The Balancing Act: The CISO View on Improving Privileged Access Controls,” visit http://www.cyberark.com/cisoview/. The CISO View report was developed in conjunction with an independent research firm, Robinson Insight.
https://www.youtube.com/watch?v=x_uFunHQ5mg
About the Report Contributors
Guest contributors include John Gelinne, Managing Director, Advisory Cyber Risk Services, Deloitte & Touche; and Gerrit Lansing, Chief Architect, CyberArk, who have worked with major organizations post-breach. We’d also like to acknowledge the security executives from large organizations that have experienced significant breaches. Due to legal constraints, these executives have contributed to this research report without attribution.
Other contributors include The CISO View panel members: Rob Bening, CISO, ING Bank; David Bruyea, Senior Vice President and CISO, CIBC; Dawn Cappelli, Vice President and CISO, Rockwell Automation; Jim Connelly, Vice President and CISO, Lockheed Martin; Dave Estlick, Senior Vice President and CISO, Starbucks; Steve Glynn, CISO, ANZ Banking Group Limited; Mark Grant, CISO, CSX Corporation; Gary Harbison, CISO, Monsanto Company; Kathy Orner, Vice President and CISO, Carlson Wagonlit Travel; Chun Meng Tee, Vice President and Head of Information Security, SGX; Munawar Valiji, Head of Information Security, News UK; and Mike Wilson, Senior Vice President and CISO, McKesson.